Case files
Real vulnerabilities, broken down: how they worked, why they got missed, and how to fix them.
 GRIMPIT LABS
Case files
The Grimpit Dispatch
Real security flaws, dissected. New case files, tools, and experiments from the crypt, delivered to your inbox.
No algorithm. No feed. Just bad code being properly reaped.
What rises from the crypt
Real vulnerabilities, broken down: how they worked, why they got missed, and how to fix them.
Scripts, labs, and tools from the Grimpit workshop, shared here before they show up anywhere else.
No roundups. No link dumps. Every dispatch is something you can actually use.
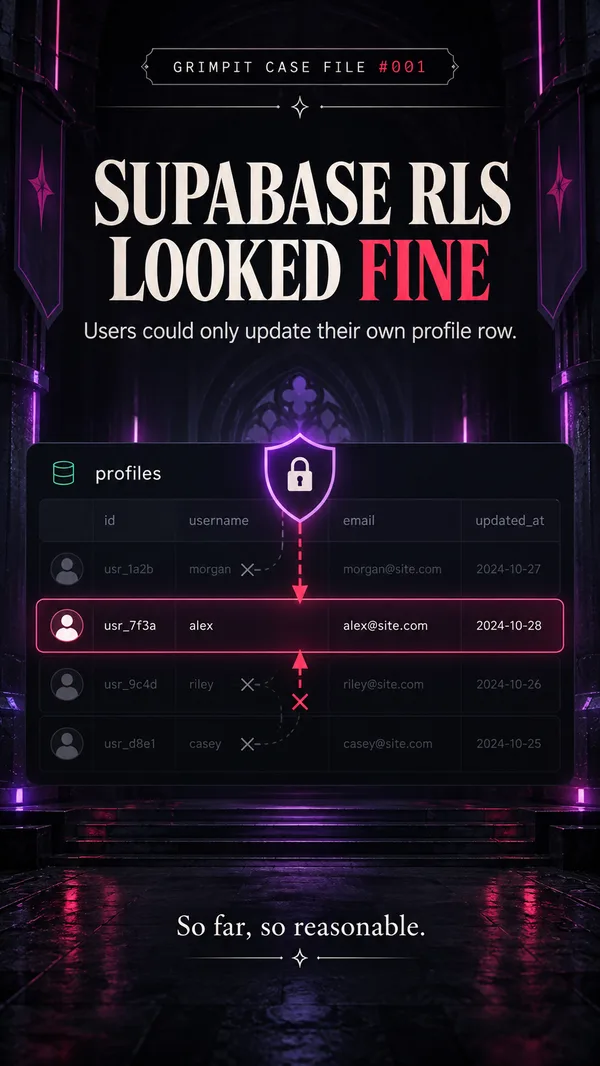
Case File #001
A Supabase Row-Level Security policy correctly limited users to updating their own profile row.
It just forgot something rather important: which columns they could update.
PATCH /rest/v1/profiles?id=eq.<uuid>

{
  "display_name": "alex",
  "role": "admin"
}
The UI hid the field. The API accepted it anyway.
Read the full case file →
Who writes this
Grimpit is the Reaper of Bad Code — a cybersecurity character focused on pentesting, AppSec, security research, tools, bugs, breaches, and the bad assumptions that make all of the above possible. Expect case files, technical breakdowns, experiments, security lessons, and the occasional autopsy of a decision that probably should not have made it to production.
From the crypt